Security
Security and control, designed in from the start
People, AI agents and your own software all reach Wyndlass through the same permission checks, approvals and audit log. Here is how we protect your organization, your screens and your data, and what we can share for your security review.
At a glance
- Hosting
- In the United States
- Encryption
- TLS 1.2 or later in transit; the primary database encrypted at rest
- Sign-in
- Password or passkey with two-factor, or single sign-on (OIDC or SAML) with SCIM
- Access
- Thirteen built-in roles, granted at places in your organization
- Audit
- Every attempt to change anything is recorded, by people and by AI
- AI
- Acts with a person’s permissions. We don’t train AI models on your data
- Screens
- Signed content and a certificate for every screen
Identity
Sign in the way your organization already does
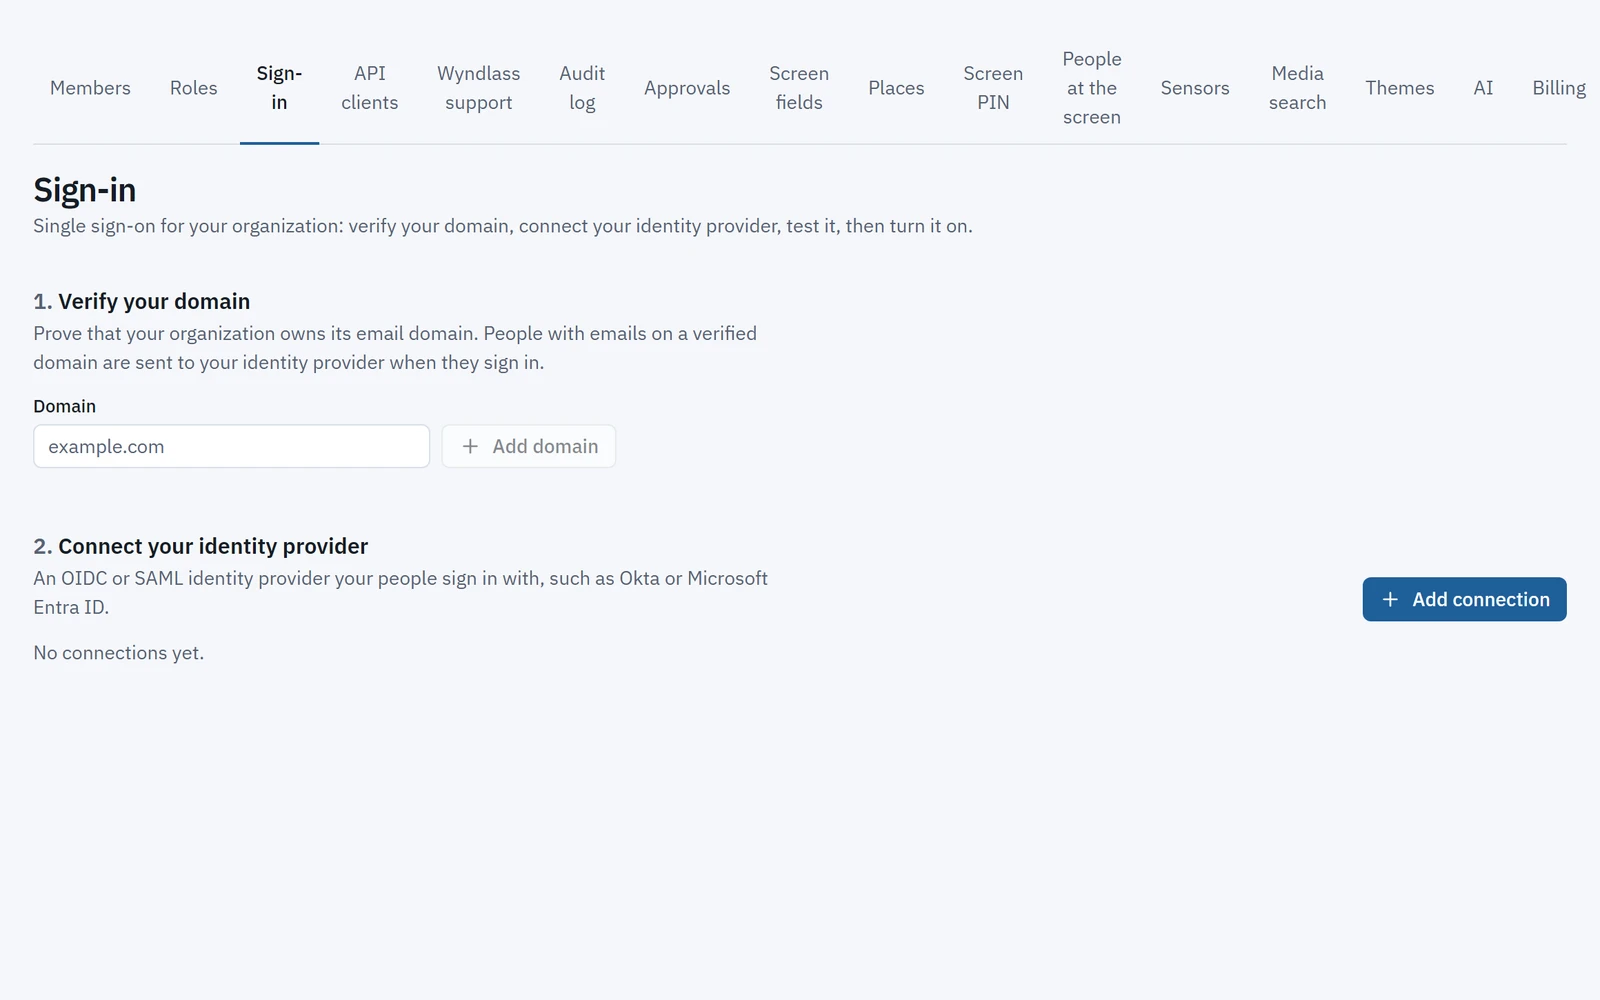
People sign in with a password or a passkey, with two-factor available, or through single sign-on with the identity provider you already use.
- OIDC or SAML per organization, with domain verification, a test sign-in and group-to-role mappings.
- Require single sign-on for everyone, with a break-glass owner kept outside it.
- Users join just in time, or are provisioned and removed by SCIM.
Access
Each person sees only their part of the network
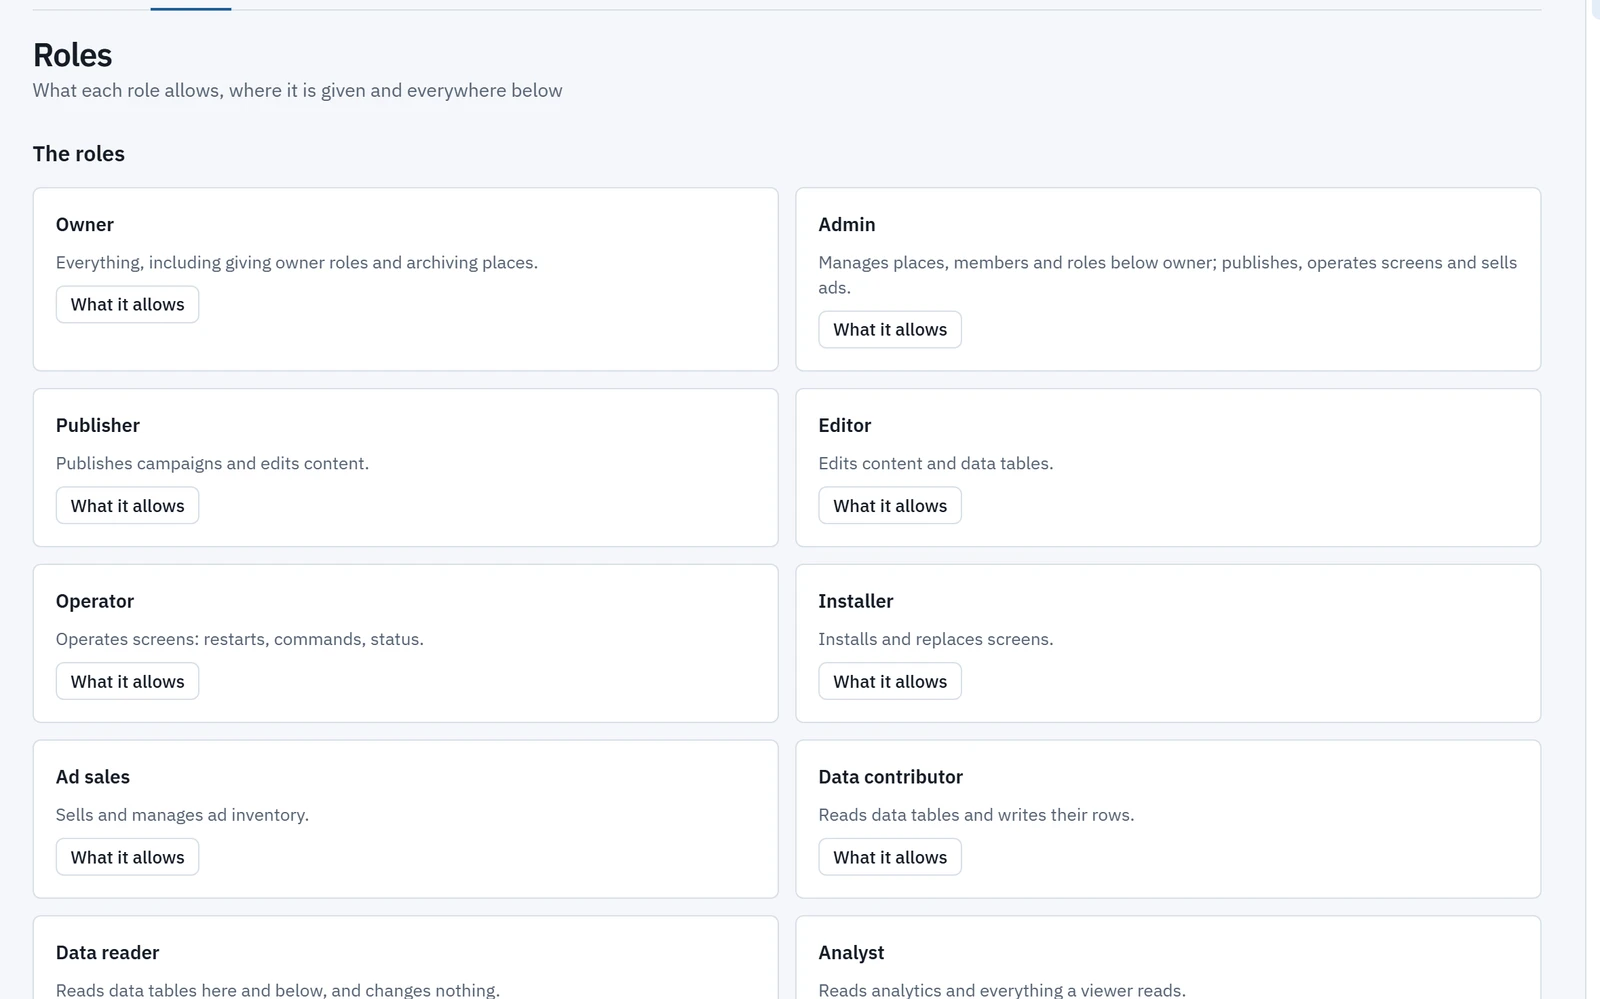
Model regions, franchisees, sites and floors as a tree of places. Roles granted at a place apply there and below, so a store manager sees their store and a regional lead sees the region.
- Thirteen built-in roles, from Owner and Approver to Installer and Data reader. A Roles page shows what each allows, down to each operation.
- Grants can end on a date.
- Removing someone is previewed first: what they lose, and which agents or API clients they own.
- API clients get their own role and toolsets, with credentials that expire after 30 to 365 days and can be rotated or revoked at any time.
The control model
Every change passes the same checks
Whether a person, an AI agent or an integration asks for it, through the CMS, the API or MCP.
Permission
The request is checked against the roles of whoever made it, at the places it touches.
Approval
Policies hold risky or wide-reaching changes for an approver, who sees the change as previewed, its reach and its risk. Nobody approves their own change.
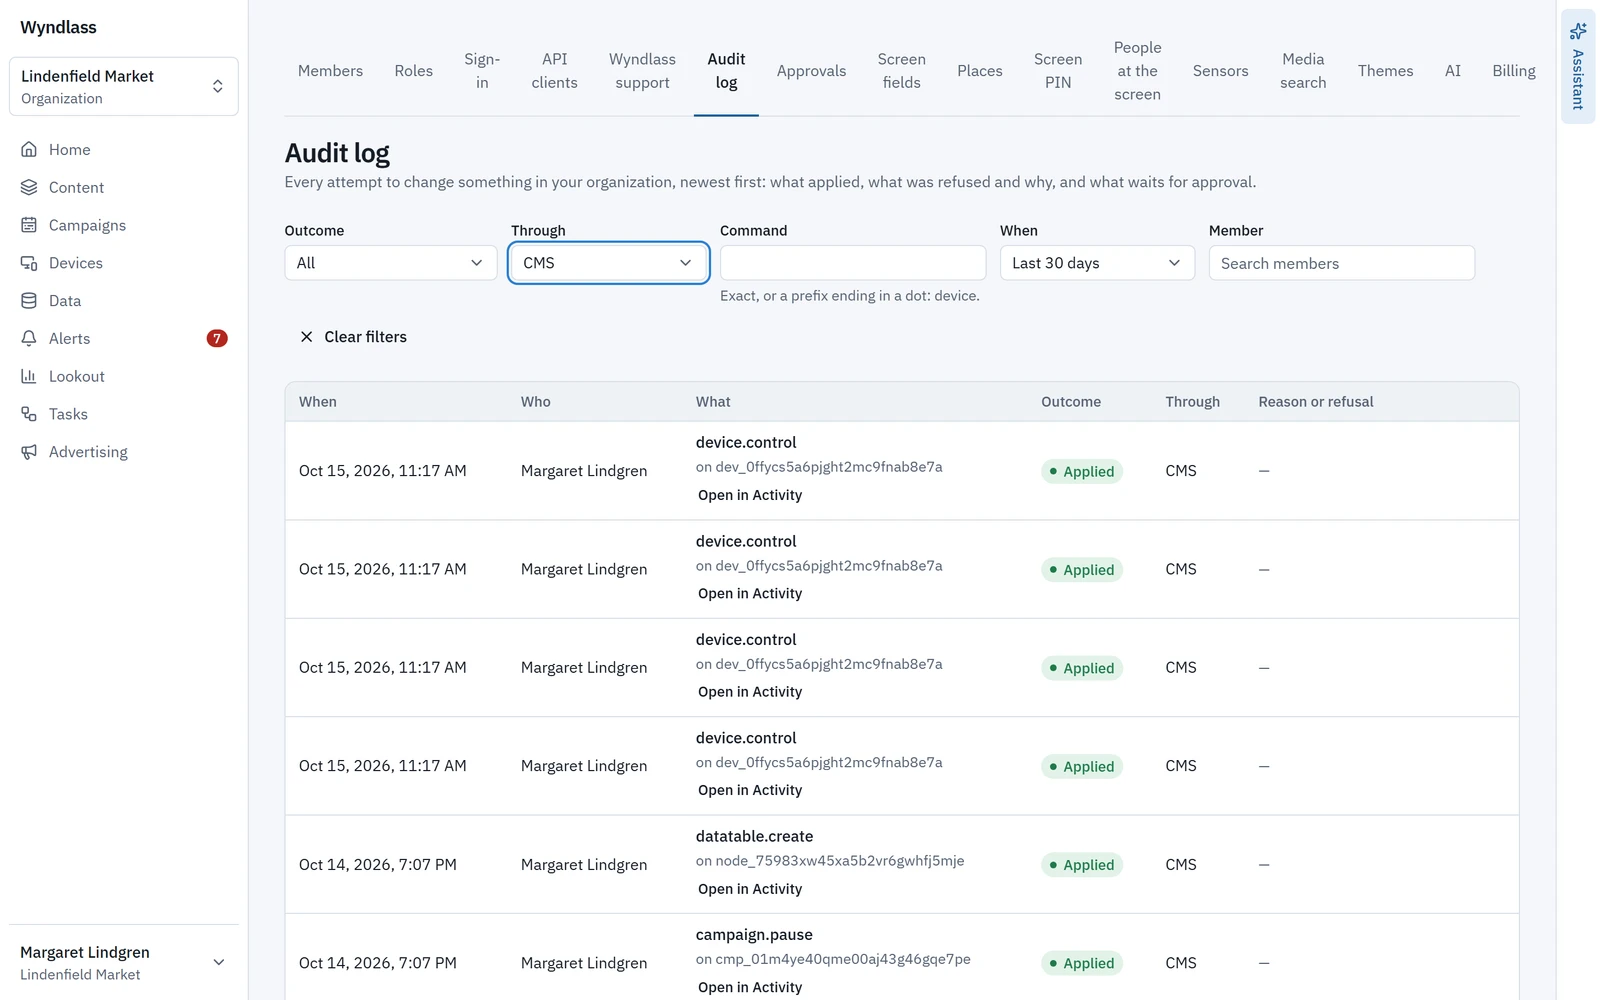
Audit
Every attempt is recorded, including those refused or held: who, through which surface, and why. Our application can only add to the log.
Undo
Recent changes can be undone in one click, within 24 hours by default. Older ones can be reverted, with a preview of anything changed since.
AI
AI works inside the same rules as your team
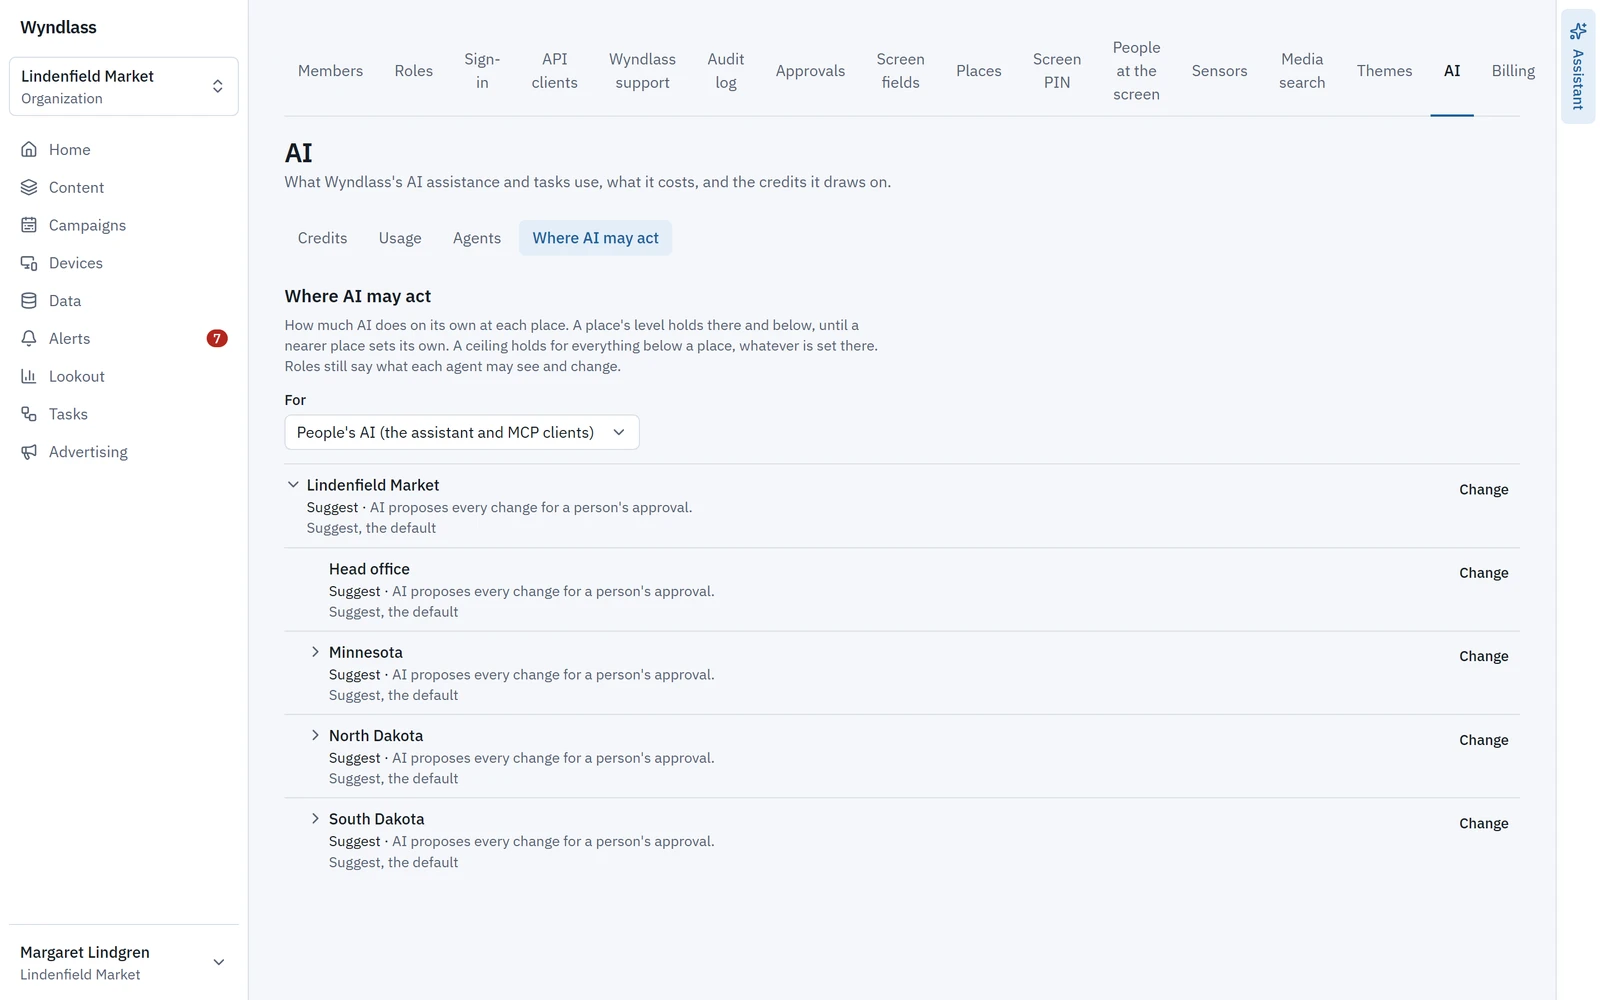
The assistant acts with the permissions of the person using it, never more. Agents have their own roles, and each place in your organization sets how far AI may go.
- Where AI may act, set per place: Observe, Suggest, Co-pilot or Autopilot. Suggest is the default, so every change AI starts on its own waits for approval. Irreversible changes always wait.
- AI never sees secrets (credentials, tokens, PINs), never grants roles or changes AI limits and approval policies, and never approves its own change.
- An agent can never be an owner, admin, approver or billing admin, and each of its actions is audited as “agent X on behalf of Y”.
- Skills, the guides your owners and admins write for your AI, steer what it does but never widen what it may do.
AI and your data
What happens to the data AI sees
Not training data
Wyndlass does not train AI models on the content or data you supply.
Kept out of our logs
We trace AI calls to keep them working, but without their prompts or answers, so those never reach our operational logs.
Your own AI tools, same rules
AI tools connect to the MCP server signed in with OAuth as the person they act for, with only the toolsets that person picks, inside the place’s AI limits.
Media indexing you can turn off
AI describes uploaded media so it can be found by meaning. Owners and admins can turn this off for the organization.
Your data
Where your data lives, and how it is protected
Hosted in the United States
Wyndlass is hosted, and processes personal information, in the United States. For personal data from the EEA, the UK and Switzerland, our DPA includes the Standard Contractual Clauses.
Encrypted
Data crossing the public internet, between browsers or screens and our services, is encrypted with TLS 1.2 or later, and our primary database is encrypted at rest.
Kept apart
Row-level security on every table in our database keeps each organization’s data apart, and tests check that one organization cannot read another’s.
Secrets stored as hashes
API client and single sign-on secrets are held by our identity provider, not in our database. SCIM tokens and screen PINs are kept only as hashes.
Support access you control
No one at Wyndlass has standing access to your organization. Support enters only with time-limited, recorded access; owners see every access, its reason and level, and can end it.
Scanned on upload
Every file you upload is scanned for malware before anything else reads it. A file that can’t be scanned is refused.
Backed up
Our database can be restored to any point in the last 35 days, and its backups are also kept in a second US region.
Archived, then purged
Deleting media, layouts, campaigns or data tables archives them first. They can be restored for 30 days, then they are purged.
Screens
Screens that play only what you sent
Every content package is signed (Ed25519) and every file hashed (SHA-256). Anything that fails a check is refused, and the current content keeps playing.
- Each screen has its own key, held in the Android Keystore and not exportable, and a 30-day certificate for mutual TLS, renewed automatically.
- A screen can be revoked, and replacing one cuts the old hardware off for good.
- The settings page on the player is locked by a PIN your workspace sets, and the CMS records what was done there.
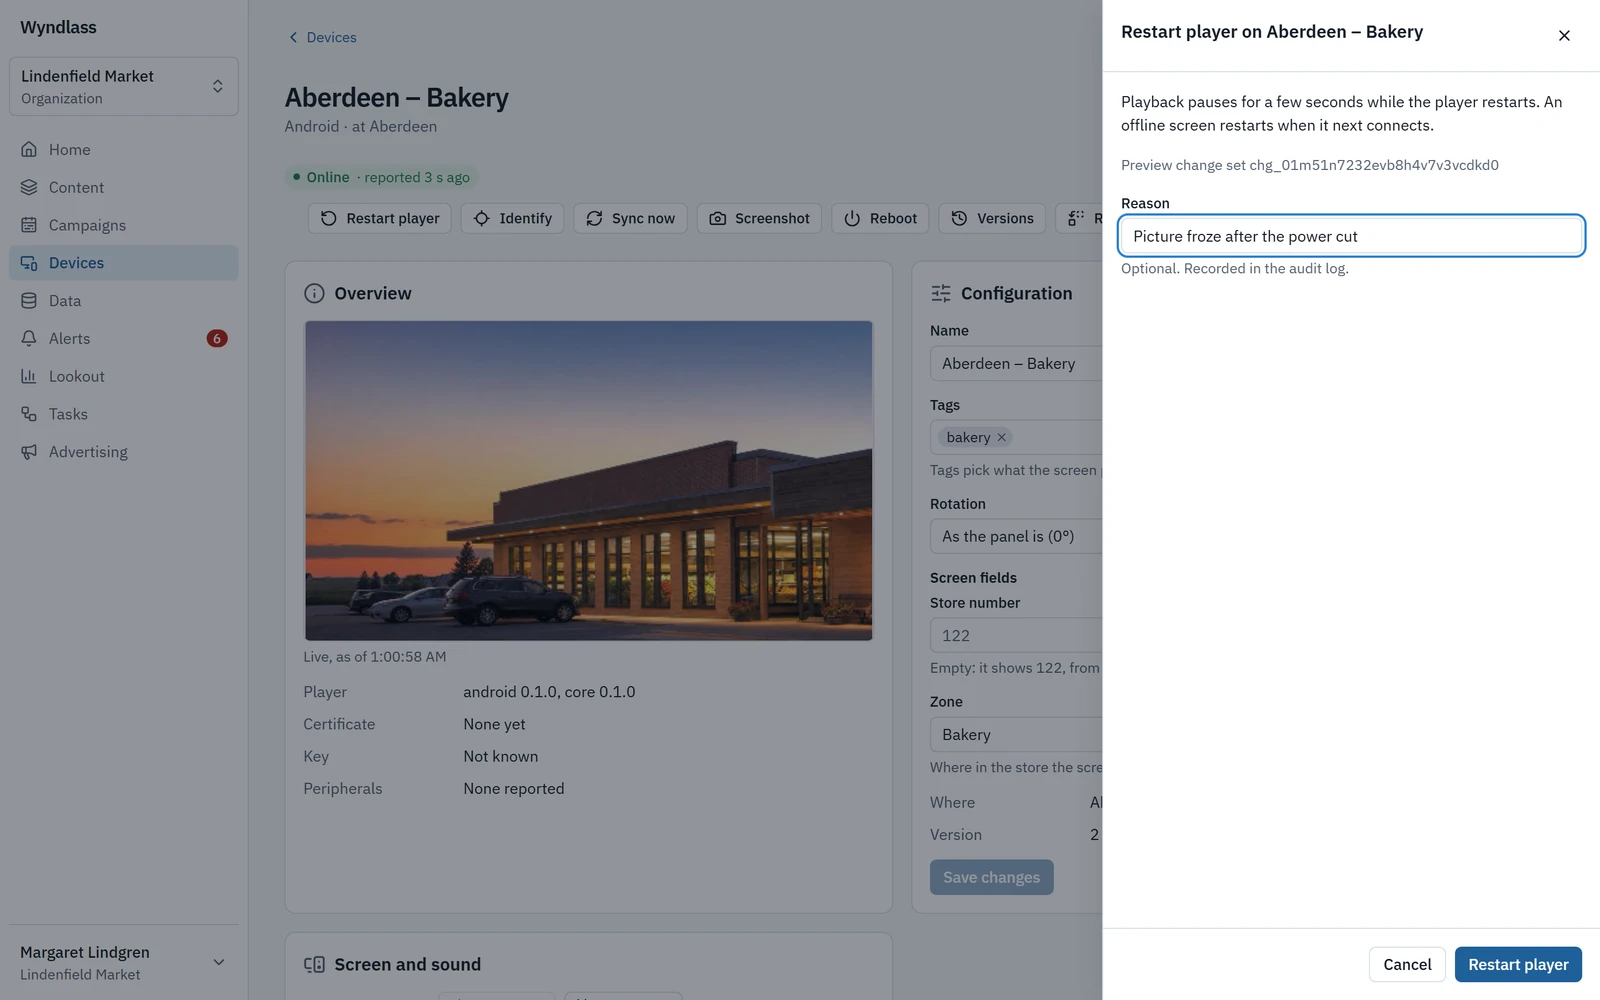
- Remote commands are previewed and confirmed, and never run twice.
Audience measurement
Counts leave the screen. Images never do.
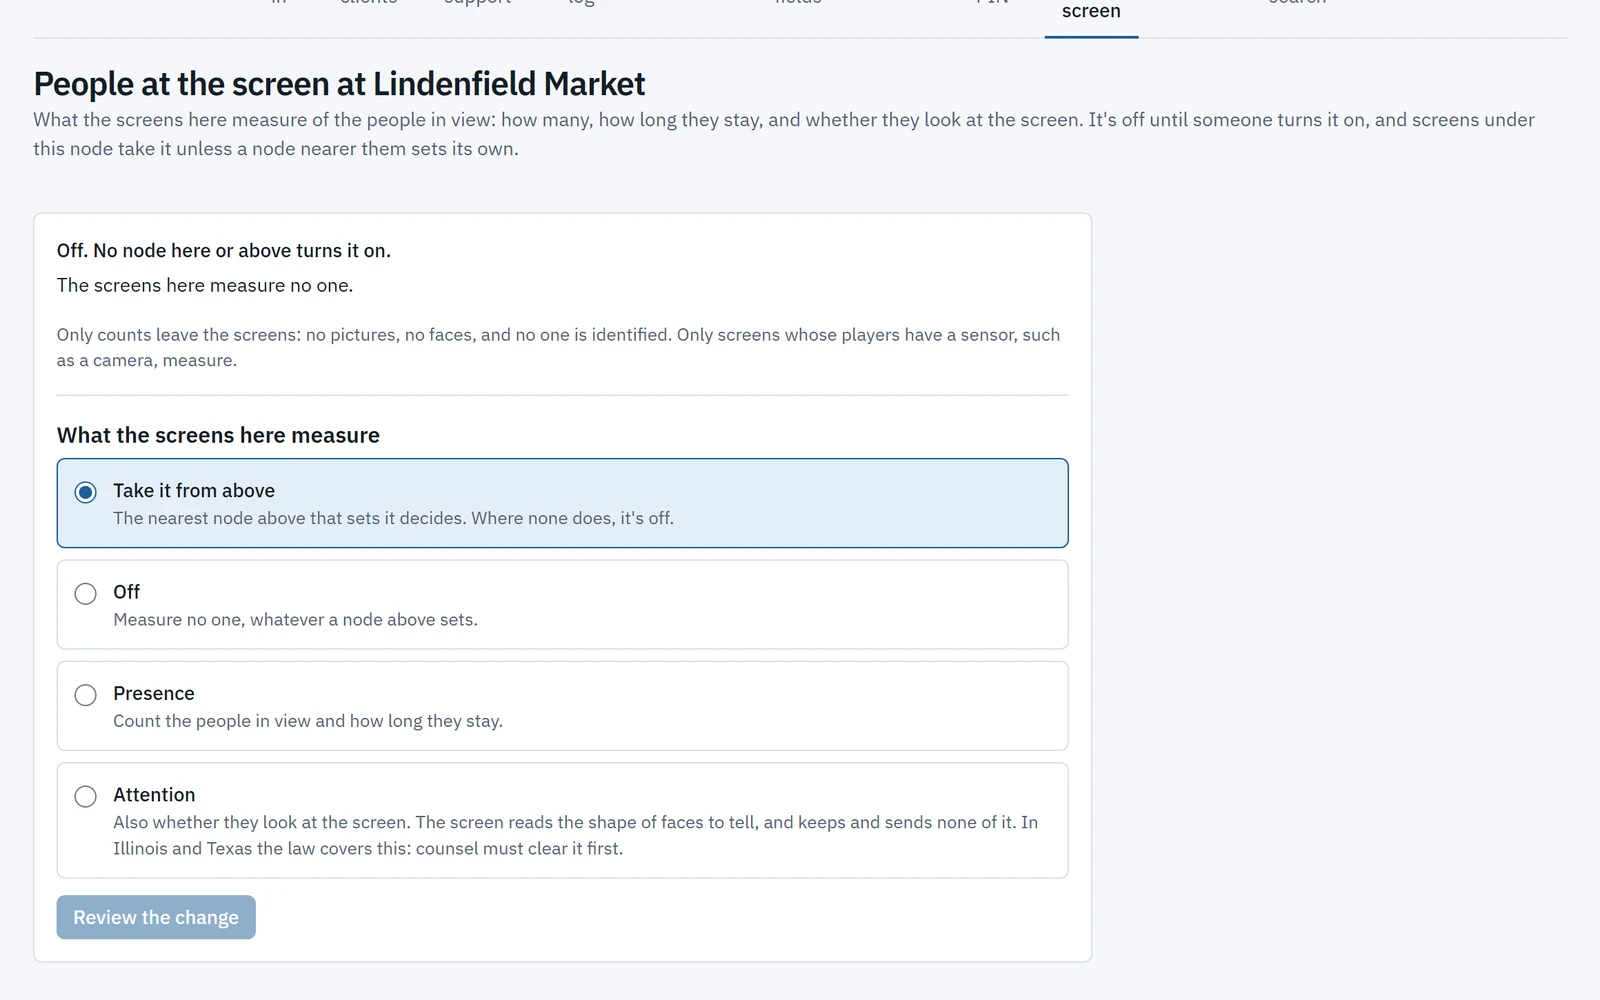
Audience measurement is off by default. Where a person turns it on for a site, the player analyses each camera frame in its memory and discards it at once. Only counts and durations leave the screen.
- Only a person, never an agent, can turn it on, after confirming that a notice is shown at the site.
- No image or video is stored or sent anywhere.
- No identification, facial recognition or emotion detection. Someone who leaves and comes back counts as a new person.
- Two modes, set per site: presence, which finds people with no face analysis, or attention, which also works out which way heads are turned.
Security reviews
What we can share for your review
This page describes the controls that are built. For the rest of your review, we share these with your security and procurement teams.
Ask your Wyndlass contact, or email legal@wyndlass.ai for the DPA and security@wyndlass.ai for anything else.
Data processing agreement
Our DPA, with the Standard Contractual Clauses and their UK and Swiss equivalents.
Subprocessors
Our current list of subprocessors, under a non-disclosure agreement.
AI models
Which AI model providers we use, and their terms, under a non-disclosure agreement.
Your questionnaire
Answers to your security questionnaire, and a call with our team for anything it does not cover.
Report a vulnerability
Vulnerability disclosure policy
We welcome reports from security researchers. If you think you have found a vulnerability in Wyndlass, please tell us.
How to report
Email security@wyndlass.ai with what you found, where, the steps to reproduce it and its impact. Our contact details are also in security.txt.
In scope
wyndlass.ai and its subdomains, the Wyndlass CMS, the API and MCP server, and the Wyndlass player software. Services run by others that we use are out of scope; please report problems in them to their owners.
While you test
- Use only accounts and data you own or are allowed to use. If you need a test organization, ask us.
- Don’t access, change or keep other people’s data. If you reach any, stop, and tell us what you saw.
- Don’t degrade the service: no denial of service, load testing or spam.
- No social engineering or phishing, and no physical attacks on our staff, our offices or our customers’ screens.
- Give us reasonable time to fix the problem before you tell anyone else about it.
What we commit to
- We confirm that we have your report within 3 business days, keep you told of our progress, and tell you when it is fixed.
- If you follow this policy in good faith, we consider your research authorized, we will not take legal action against you or ask anyone else to, and if a third party does, we will make it known that you acted under this policy.
- We don’t pay bounties, but we are glad to credit you once the problem is fixed, if you want us to.
Security: common questions
What about SOC 2?
We are working towards SOC 2. For your review today, we share our DPA and subprocessor list and answer security questionnaires, and this page describes the controls that are built.
Where is our data stored?
In the United States. Wyndlass is hosted there, and we process personal information there. Content reaches your screens through a content delivery network, which may cache it nearer to them.
Do you train AI models on our data?
No. Wyndlass does not train AI models on the content or data you supply.
Can Wyndlass staff see our data?
Only with time-limited, recorded access: no one at Wyndlass has standing access to your organization. Owners see every access, its reason and level, and can end it.
Can we require single sign-on?
Yes. Connect an OIDC or SAML identity provider, then require SSO for everyone, with a break-glass owner kept outside it. People can join just in time or be provisioned and removed by SCIM.
Will you tell us about a breach?
Yes. If a security breach affects your content, we notify you without undue delay, and within 72 hours of confirming it.
What happens to our data if we leave?
When your account is closed, we schedule the deletion of your content for 30 days later. Until then you can ask us to restore access so you can export it with the export tools and the API. Deleted data leaves our backups as they expire, within 12 weeks.
How do we report a vulnerability?
Email security@wyndlass.ai with what you found and how to reproduce it. Our vulnerability disclosure policy on this page sets out the scope, the rules and our commitments.
See the controls for yourself
Access is by invitation during launch. Request a demo and we will walk your team through roles, approvals and the audit log.